Get started
Copy link to the page “Get started”Follow the steps from installation to the first certificate that is installed and renewed automatically on one of your servers.
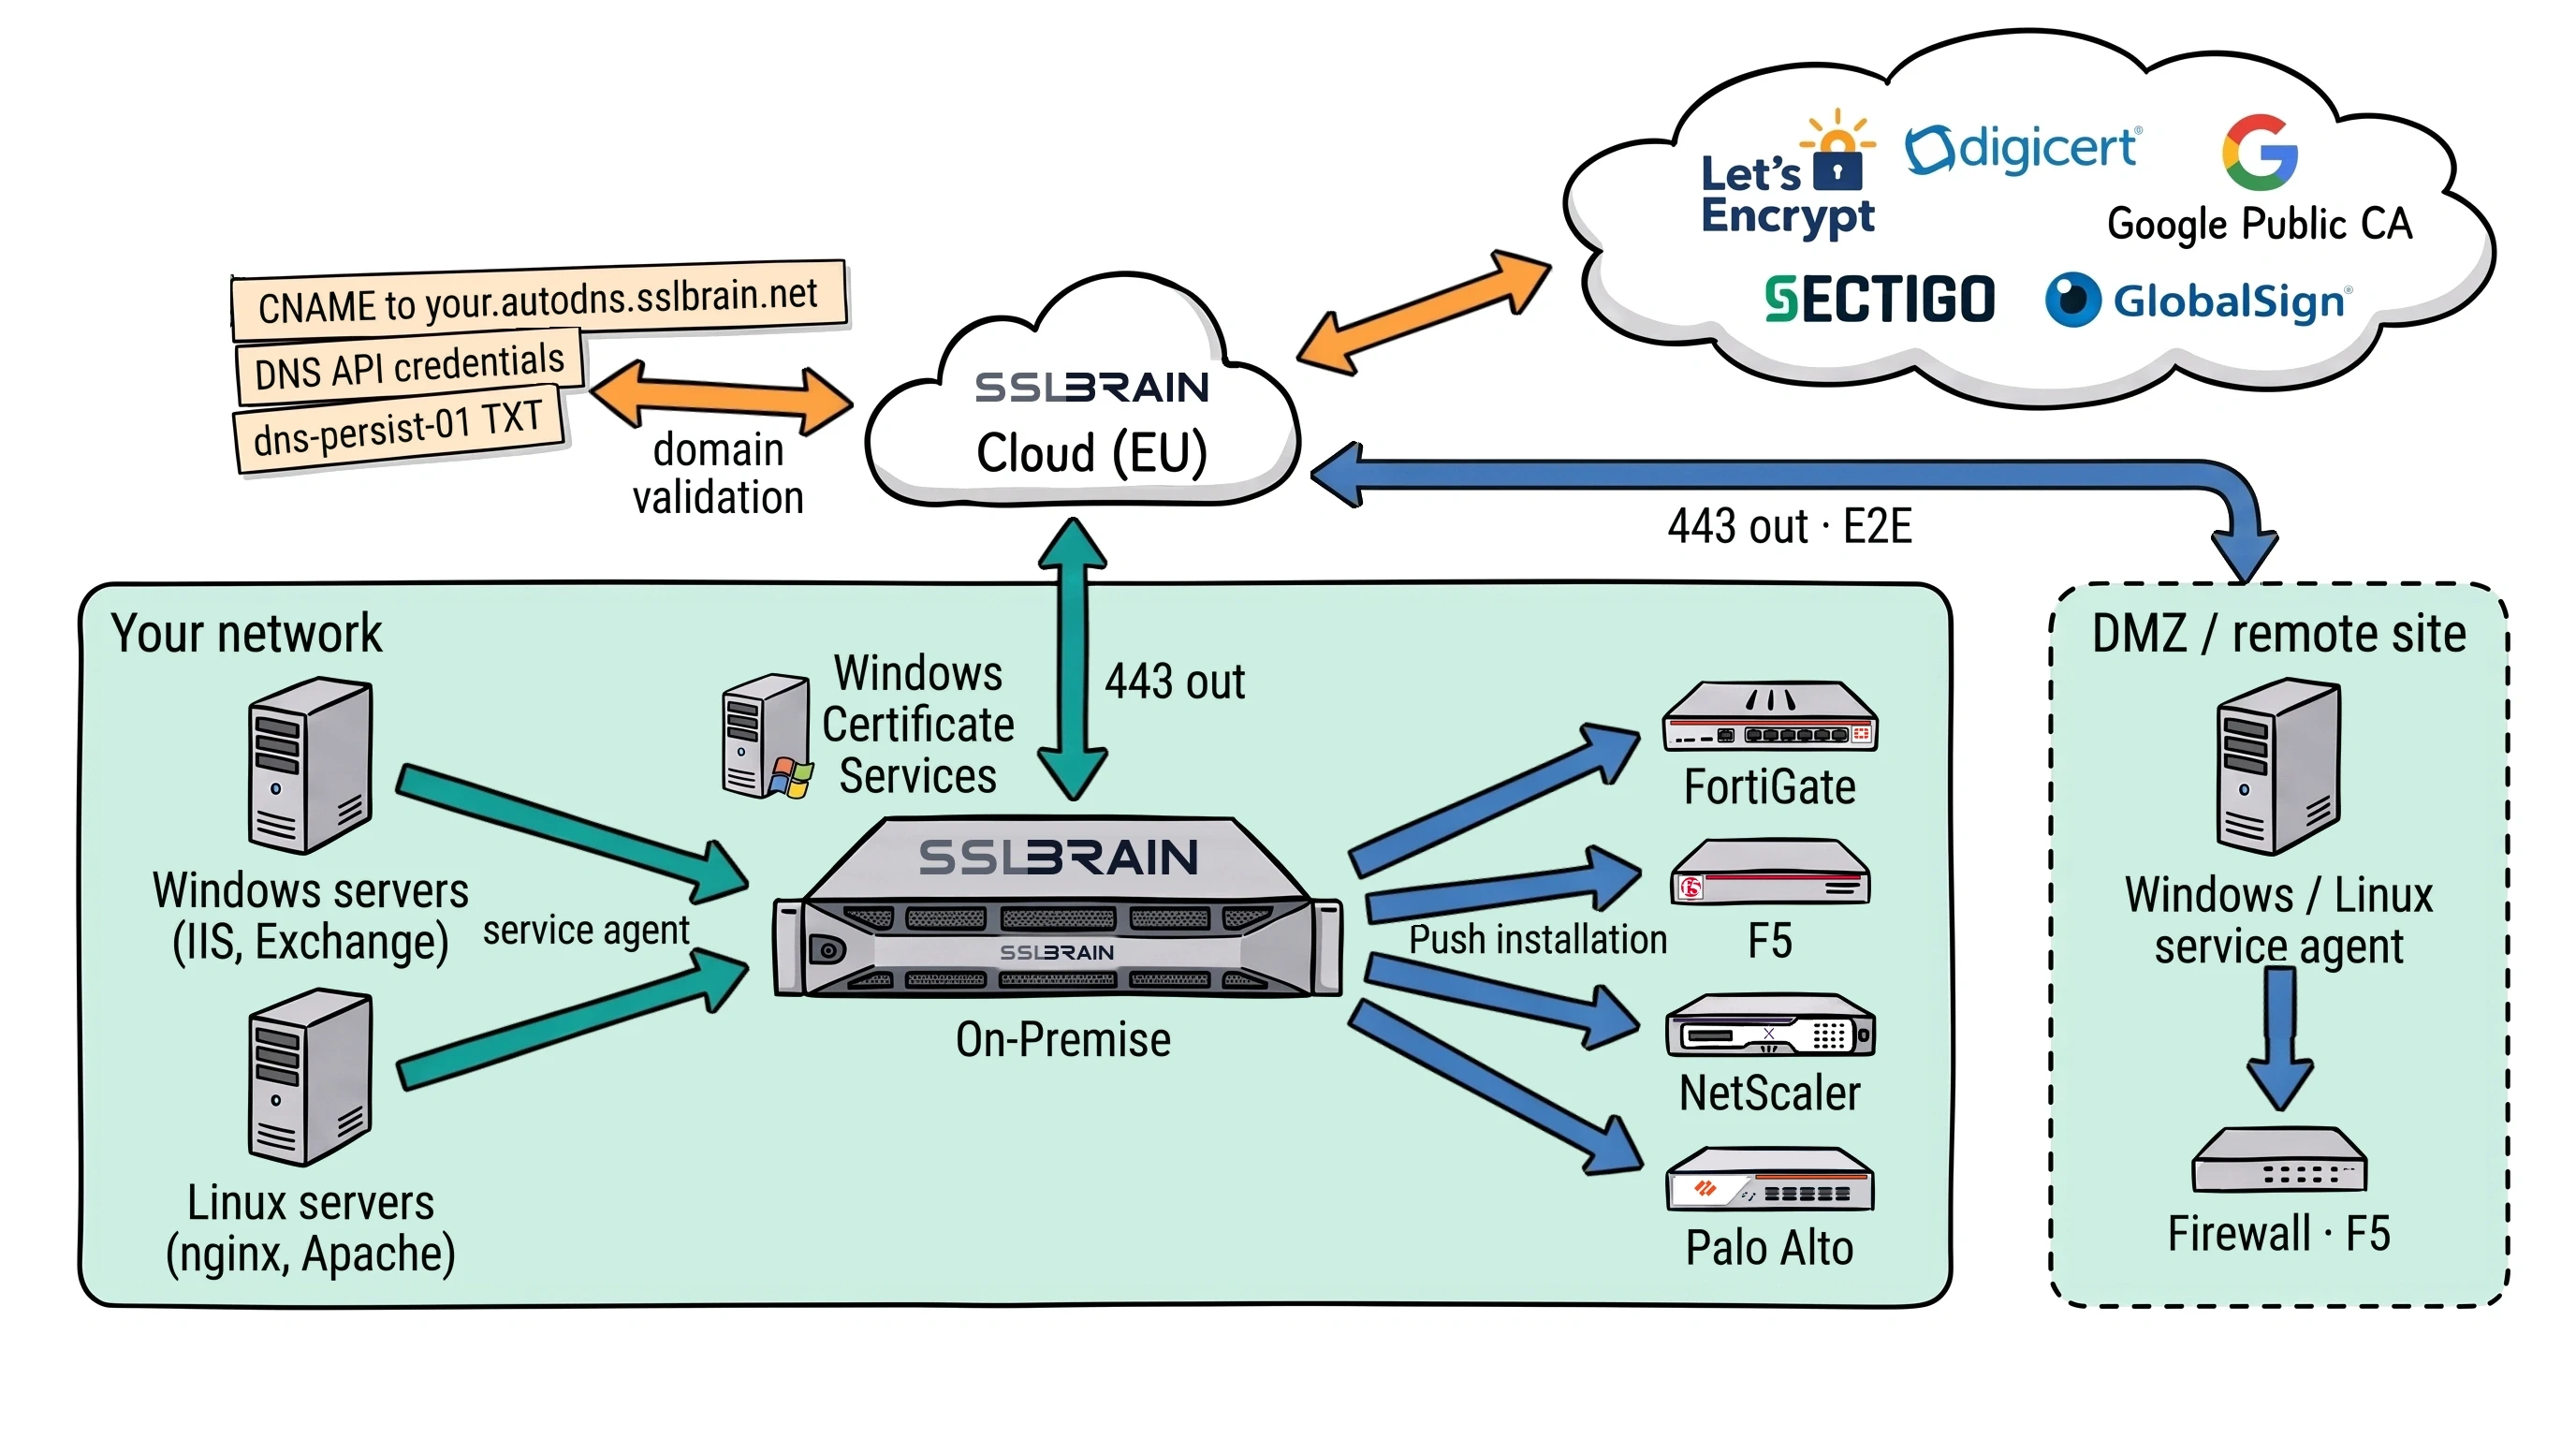
- Your network: sslbrain On-Premise runs here and generates the private keys, and sslbrain Cloud (EU) never sees them. On-Premise talks only to Cloud, outbound on port 443.
- Domain validation: a CNAME to your.autodns.sslbrain.net, access to your DNS provider’s API, or a dns-persist-01 TXT record.
- CA: your choice of Let’s Encrypt, DigiCert, Google Public CA, Sectigo or GlobalSign, or your own Windows Certificate Services. Cloud talks to the CA and to DNS.
- Service agent: Windows and Linux servers fetch them from On-Premise on port 443.
- Push installation: devices without a service agent get their certificates from On-Premise, for example FortiGate, F5, NetScaler, Palo Alto and other equipment.
- Remote site: a service agent in a DMZ or at a remote site connects via sslbrain Cloud (EU), outbound on port 443 and E2E, with no connection to your network.
What you need
Copy link to the section “What you need”- An sslbrain Cloud (EU) account where you are an owner or administrator.
- Space for the appliance on a virtual machine or a Linux server with Docker.
- Administrator access to the server that will receive the certificate.
From installation to your first certificate
Copy link to the section “From installation to your first certificate”Start at step 1 and follow the next step on each page. You can skip step 4.
- 1. Install sslbrain Install the appliance as a virtual machine in VMware, Proxmox or KVM, or in Docker on your own Linux server, and open it in your browser.
- 2. First-time setup Connect the appliance to your account, choose a licence, save the 12 backup words and enable automatic maintenance.
- 3. A name and certificate for the appliance Give the appliance the free name under my.sslbrain.net, and it gets a trusted certificate with nothing more for you to do.
- 4. Find the certificates you already have Optional: scan the network and see which servers answer with TLS and when their certificates expire.
- 5. Connect servers Connect your servers, find their services and certificates, and see which servers need an installation plan.
- 6. Prove the domain is yours Prepare your domain with AutoDNS (CNAME) and check the result. Find DNS-API and other validation methods when your setup requires them.
- 7. Choose where certificates come from Use sslbrain Cloud without CA setup, or choose Custom ACME, Internal CA or Manual import. See how certificate profiles connect to installation plans.
- 8. First certificate on a server Create an installation plan from your server's proposals, follow the run and check the certificate served by the service. Renewals install automatically.
Tasks on the appliance home page
Copy link to the section “Tasks on the appliance home page”Under Getting started, each task gets a tick when it is completed:
- Connect a server.
- Make a domain ready.
- Create installation plans automatically.
Check the installed certificate as described in step 8. If the appliance cannot reach the server, see Servers outside your network.
Larger environments
Copy link to the section “Larger environments”Find the guide for your situation.
- Roll out the service agent to many Windows servers Roll out the service agent to Windows servers with a GPO, try it on one server and check the result in the appliance.
- Domains without a DNS API Use AutoDNS (CNAME) without a DNS API. Find fields for your own DNS server with RFC 2136, a REST provider or a script when validation requires it.
- Internal certificates from Windows CA Connect Windows CA as an internal certificate source, create the installation plan and check issuance. Resolve access failures and pending requests.
- Sign-in with Active Directory Let colleagues sign in to the appliance with their AD account, and give them a role based on their AD group.
- When the appliance is down Bring the appliance back into service, check renewals and see what keeps working during an outage.
- Servers sslbrain does not know Use your own integration to install certificates for a service the catalogue integrations do not cover.
- Move or restore the appliance Restore data from a backup file on the same or another machine, and see what to do without a usable backup.
- Audit and compliance Find changes in the audit log, export them, send every row to your SIEM and check the chain against sslbrain Cloud.
Operations
Copy link to the section “Operations”Keep track of certificates, updates and backups.
- Keep an eye on your certificates Get alerts by email, webhook, chat or an on-call service when certificates or servers need action. Set up channels and alert rules in sslbrain.
- Keep sslbrain up to date Update the appliance to a signed version, choose what updates by itself, and update from the console if the web interface does not respond.
- Save a backup and restore from it Back up the appliance's data and keys, keep a copy off the appliance, and return the appliance to the moment the backup was taken.
- When something does not work Look up what the appliance shows you, and find the cause and what to do about it.
Reference
Copy link to the section “Reference”Look up features and settings.
- Integrations Find the integration for your service, check the installed version and approve a signed version in the catalogue.
- Your own integrations Upload your own integration, allow it on the server and find agent.yml requirements, examples and variables.
- Users and sign-in Sign in with sslbrain Cloud or a local password, add colleagues with the right role, and keep track of the licence's logins.
- Security How the appliance protects the private keys, what the 12 backup words open, which data is sent out, what happens if something is compromised, and which ports must be open.
- Policy and audit Check automation settings, allow your own integrations on servers, see the Free domain limit and find the audit log.
- Console menu Every item in the virtual appliance's console menu: status, network, logs, restart, update, disk space and Danger zone.
- sslbrain Cloud Your sslbrain Cloud account: appliances, installation files and requirements, licences and units, team, and moving a licence to another appliance.
- Support and diagnostics Send a support bundle to FairSSL, share diagnostics, approve a support partner, and open SSH for troubleshooting for 24 hours.
- Tools Read a certificate, convert between PEM, PFX, DER and JKS, create and look up CAA records, and make a self-signed certificate for testing.
- Modules Download and activate licensed modules, use Windows CA and MitID certificates, and set service windows.