Built for real infrastructure
The appliance manages certificates across Windows and Linux servers, supports multiple certificate authorities, and automates the entire lifecycle.
Shorter lifetimes, more renewals
Certificate lifetimes are getting shorter, and will get shorter again. The CA/Browser Forum has binding deadlines that step the maximum lifetime down in three phases through 2029.
Maximum lifetime and DCV reuse since March 2026.
Next step. Lifetime and DCV reuse are halved.
Final target. DCV reuse drops to 10 days, so domain validation runs every renewal.

The same 50 servers. More certificate work. Let sslbrain handle it.
With 50 servers and 47-day certificates that becomes around 570 renewals per year¹ . The appliance uses a central scheduler that scales automatically regardless of how short lifetimes become.
Read more about the 47-day timelineSwitch CA without touching a server
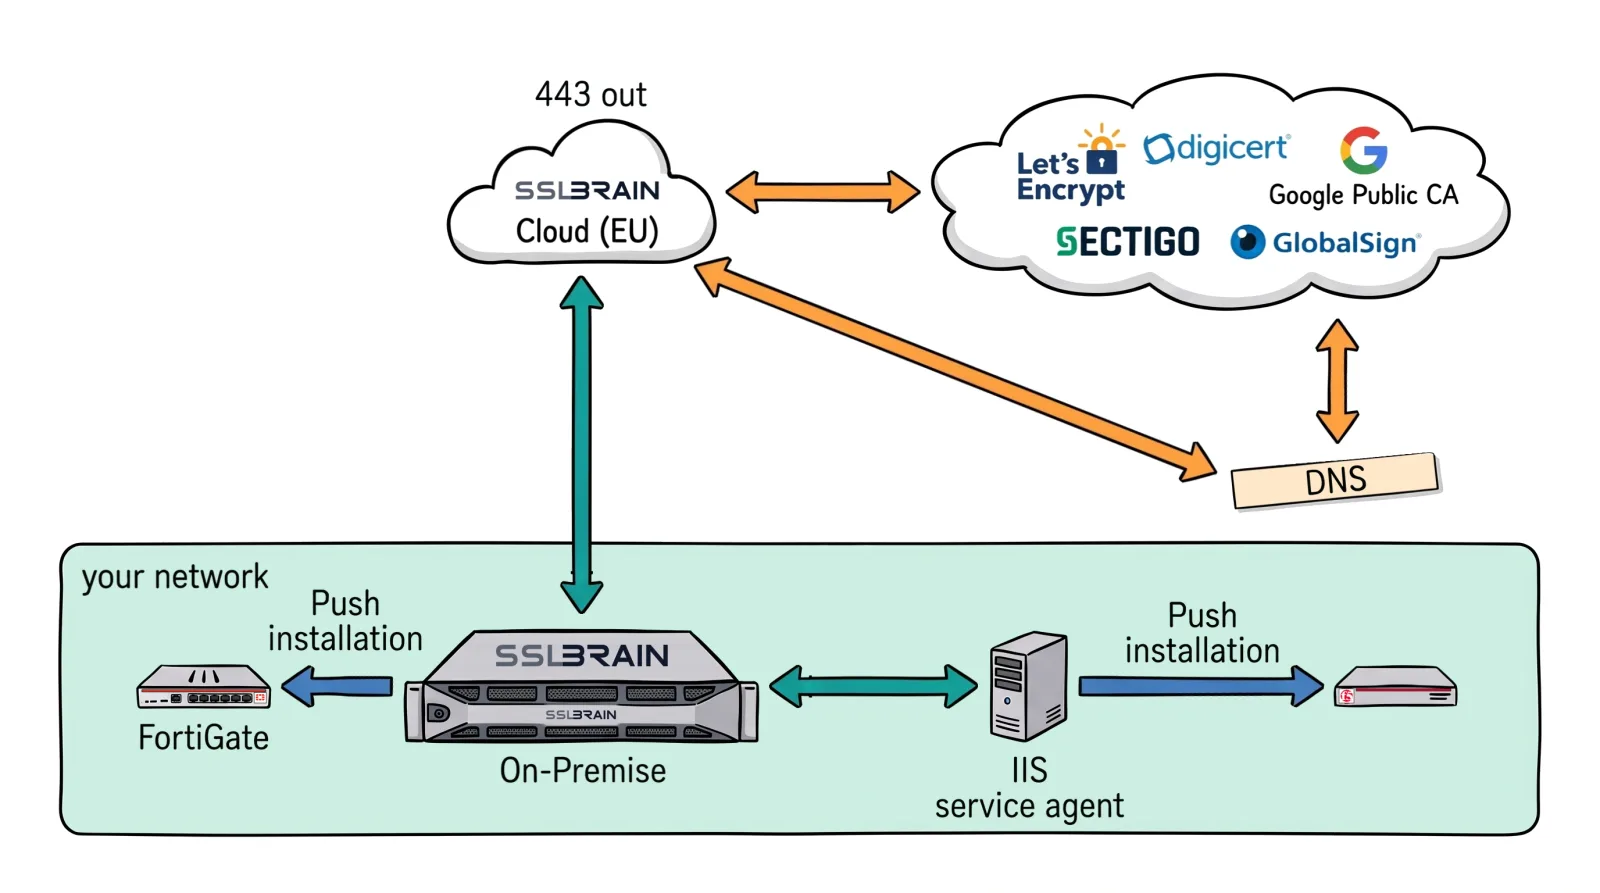
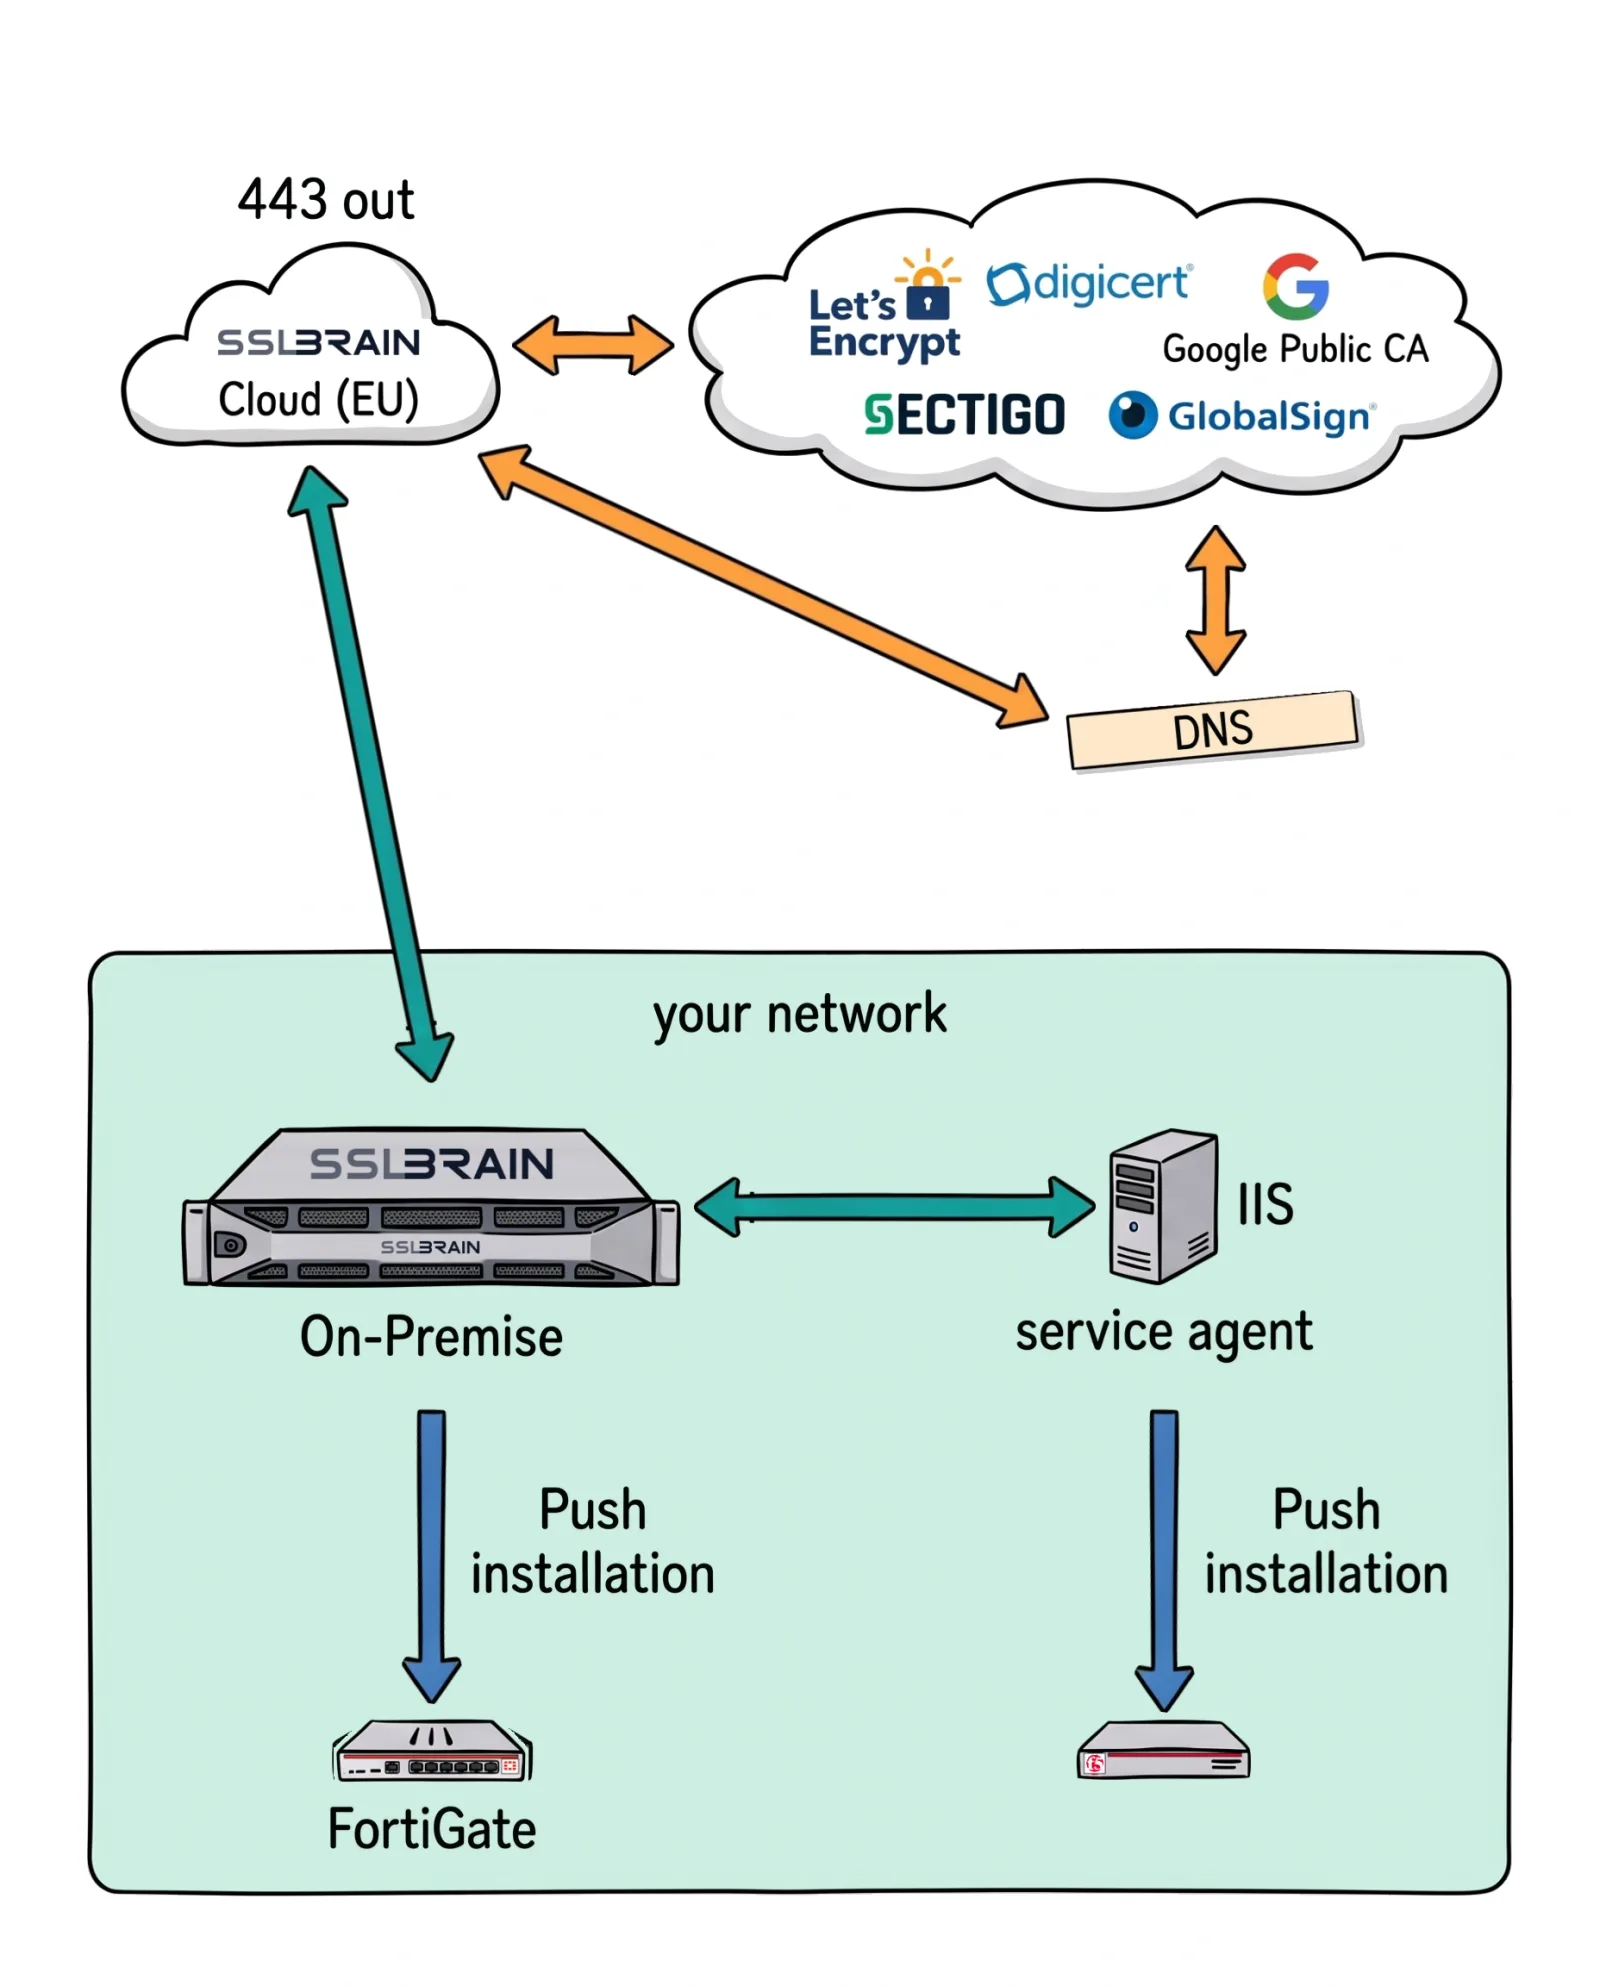
The appliance communicates with the CAs and installs the certificates on your servers through signed integrations. If a CA changes its API, standards, or pricing, we update the connection and your servers notice nothing.
You can switch between Let's Encrypt, Google Trust Services, DigiCert, Sectigo and GlobalSign without changing configuration on a single server. The appliance absorbs the complexity.
Certificate Sources
We support any ACME-based CA.
- Let's Encrypt (ACME)
- Google Trust Services (ACME)
- DigiCert
- Sectigo
- GlobalSign Atlas
- Internal CA
- Custom CA
Servers
Deploy certificates to any server platform.
- Microsoft IIS (Windows Server)
- Apache HTTP Server
- Nginx
- HAProxy
- Tomcat / Java Keystore
- FortiGate / FortiMail
- Citrix NetScaler
- Microsoft Exchange
- Any server via your own integrations
Protocol Support
Industry-standard protocols for validation and deployment.
- ACME (RFC 8555)
- DNS-01 validation with AutoDNS (CNAME)
- HTTP-01 validation
- SSH-based deployment
- REST API integration
Lifecycle Management
Automate the entire certificate lifecycle.
- Automatic DNS-based validation
- Automatic certificate discovery
- Expiry monitoring & alerts
- Automated renewal
- Multi-domain (SAN) certificates
- Wildcard certificates
- Certificate revocation
Security
Enterprise-grade security built in.
- On-Premise. Your data stays on your network
- Data encrypted by rotating online vault key
- Code running on your network is visible and inspectable
- Every catalogue integration security inspected and signed by FairSSL
- Own key pair per service agent, messages encrypted with AES-256-GCM
- Scripts executed via stdin, never written to disk
- Role-based access control
- Audit logging
Operations
Simple to deploy and operate.
- One appliance (OVA/KVM or Docker)
- SQLite database (zero config)
- Setup wizard (3-minute onboarding)
- Web-based management UI
- Architecture with integrations
- Update integrations and sslbrain via sslbrain Cloud (EU)
- Fixed IPs for firewall whitelisting
Explore the features in depth
Each core capability explained the way it works in practice.
Automatic renewal
The appliance renews your certificates in the CA's recommended window or at 75% of lifetime and installs them where they are used. Shorter lifetimes stop being your problem.
Read moreNetwork discovery
Scan your IP ranges and find every TLS certificate in the environment, including the ones nobody documented. Visibility before automation.
Read moreIntegrations
Signed integrations install certificates on Windows, Linux, network appliances, and cloud platforms. The catalog lists 80 integrations. Push or pull, your choice.
Read moreLeast privilege in practice
The service agent on the server never receives SSH keys or sudo from the appliance. It only runs signed tasks, and you decide how much privilege it holds.
Read moreACME and AutoDNS (CNAME)
The appliance speaks ACME to the CAs and answers domain validation automatically. Your servers never run their own ACME clients.
Read moreOn-Premise appliance
You run sslbrain as a virtual machine (OVA or KVM) or in Docker inside your network. Private keys and credentials stay on the appliance.
Read moreSource-available code
Every line of code can be inspected, and every integration is signed with a YubiKey. Trust in a security product should be verifiable.
Read moreDNS-PERSIST-01 without DNS keys
One TXT record per domain, published once. After that, sslbrain issues certificates immediately, and no server, agent or appliance holds a DNS API key.
Read moreIntegrations
The appliance installs certificates on Windows and Linux servers, load balancers, firewalls, storage and cloud services. The wheel leads to the overview, where each integration has its own page on how the certificate gets there. There you can search and pick a category and how it installs.
80 systems we install on
See all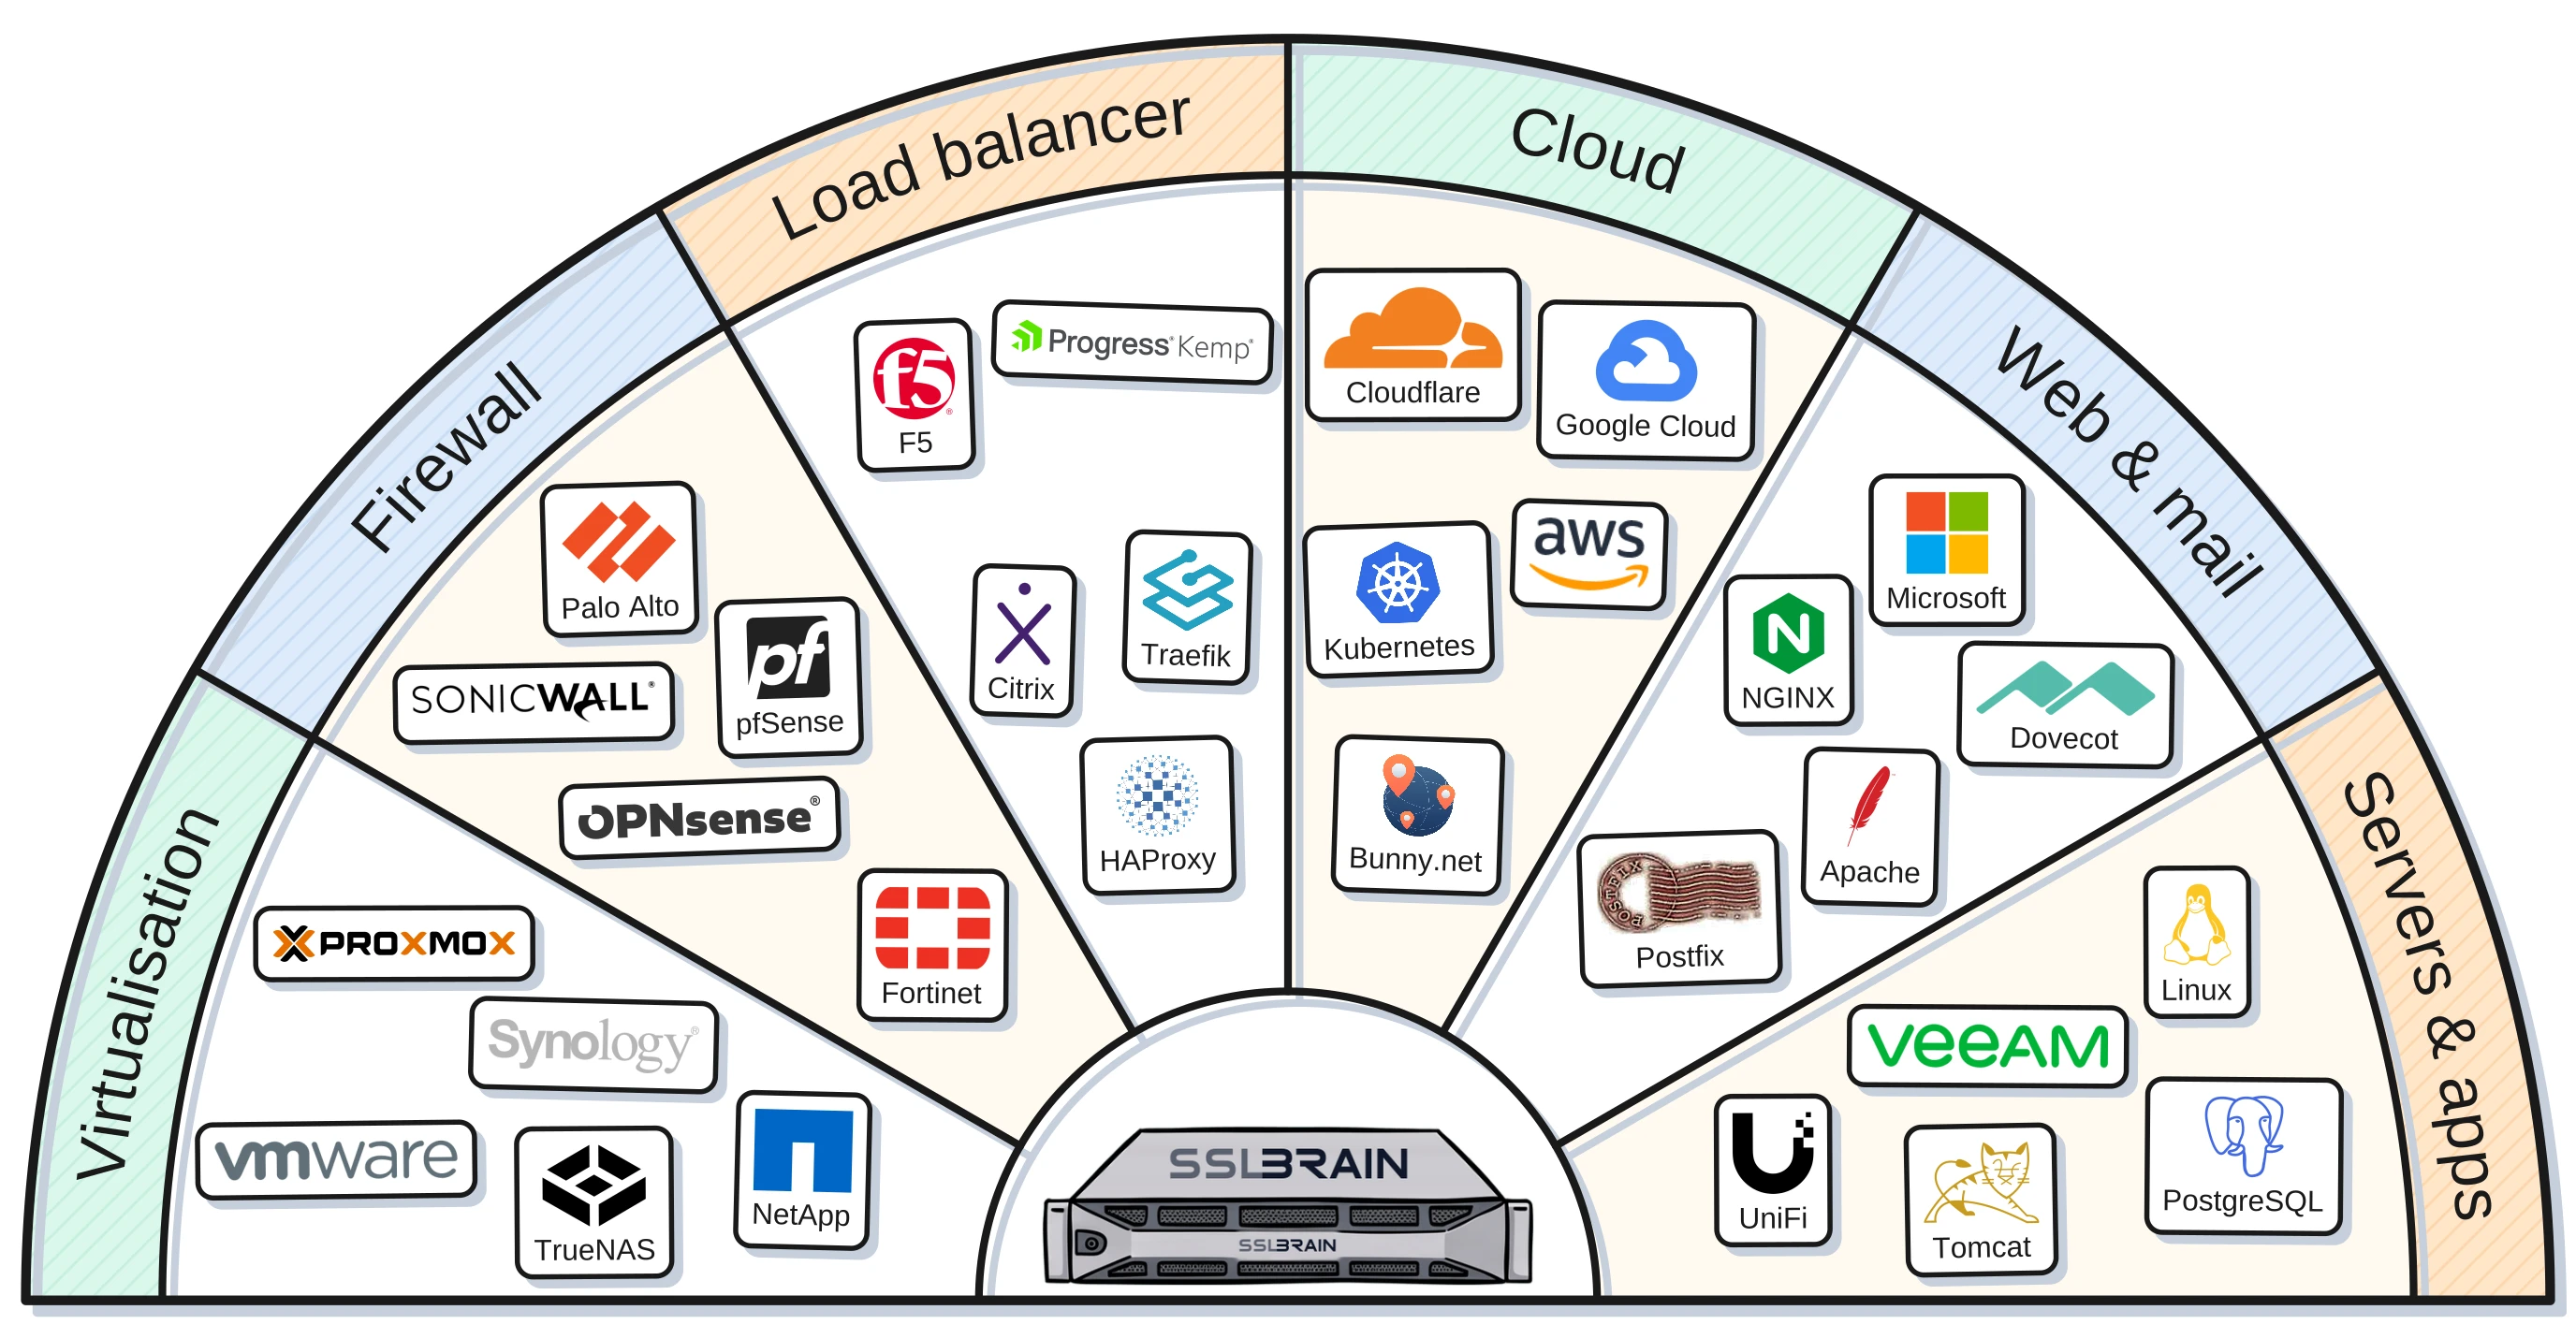
Architecture with integrations
The appliance uses YAML-defined integrations to handle certificate deployment. Each integration is a set of platform-specific scripts that run on the server. This approach means:
Windows service agent (.NET 9, pull-based)
No inbound ports required. Pulls signed tasks over HTTPS. The install code is used only for the first enrolment; after that the service agent has its own key pair, and every message is signed and encrypted with AES-256-GCM.
Secure integration execution
Scripts are executed via stdin piping directly to the interpreter. No script files are written to disk. Secrets are passed via environment variables, never as command-line arguments.
Security you can verify
The appliance is designed to be transparent. All code is visible and inspectable.
YubiKey-signed integrations
Every integration in the catalogue is written, reviewed and signed by us. A suggestion from a user becomes an integration only after we have reviewed it, locked the code and released it under FairSSL's signature. All scripts are visible on GitHub and can be inspected.
You decide what runs
Every server has a ScriptPolicy that decides what it accepts. By default the service agents run only integrations and scripts signed with FairSSL's hardware key. Your own integrations run only where you switch them on. The policy is set on the server and can be locked via Group Policy.
Least privilege by default
The recommended service agent never receives SSH keys or sudo from the appliance and only executes signature-verified tasks. How much privilege the service holds locally is your call: root for simplicity, or a scoped service user with access to one service's certificate files and one reload command.
Read about least privilege in practiceYour data stays on the appliance
Cloud cannot fetch or see your data
Stolen copy is useless
NIS2 documentation
NIS2 requires documented, monitored, and auditable security processes. A cron job is not a documented process. The appliance provides the structure and evidence that NIS2 demands for certificate management.
Ready to automate your certificates?
Get started in under 5 minutes with the Free plan.
The developer of sslbrain is FairSSL A/S, a Danish company with 16 years of experience in the SSL certificate industry.