Free
5 servers, 10 installation plans and up to 2 domains, with free certificates from Let's Encrypt and Google. Free costs nothing and needs no credit card.
Need Basic, Professional or Enterprise? Choose your edition after creating the account.
Create free accountCreate an account
Create a free sslbrain Cloud (EU) account. The account holds your license, downloads, and the status of your installations.
Run the installer
On your Linux server, run bash <(curl -fsSL https://sslbrain.com/install.sh). It supports x86 and ARM, installs Docker if missing, and installs the appliance and the host controller with its cron entry. The controller keeps the appliance updated.
Activate the licence
Open the appliance in your browser at the address the installer shows. Log in with your sslbrain Cloud account in the appliance’s own web interface to activate the licence.
No credit card.
Outbound only
The service makes outbound connections to fixed sslbrain addresses, so no inbound ports from the internet are required.
All data local
Private keys, credentials and the rest of your data stay on the appliance. Cloud cannot fetch or see them.
Uninstallation
Stop the container and remove the volume, and there are no leftovers. The account can be re-used later.
System requirements
Minimum
- Docker Engine 24+ or Docker Desktop
- 4 GB RAM
- 20 GB disk space for Docker, 40 GB for the virtual appliance
- x86_64 or ARM64 architecture
Recommended
- 8 GB RAM for 25+ servers
- SSD storage for better performance
- Dedicated host or VM
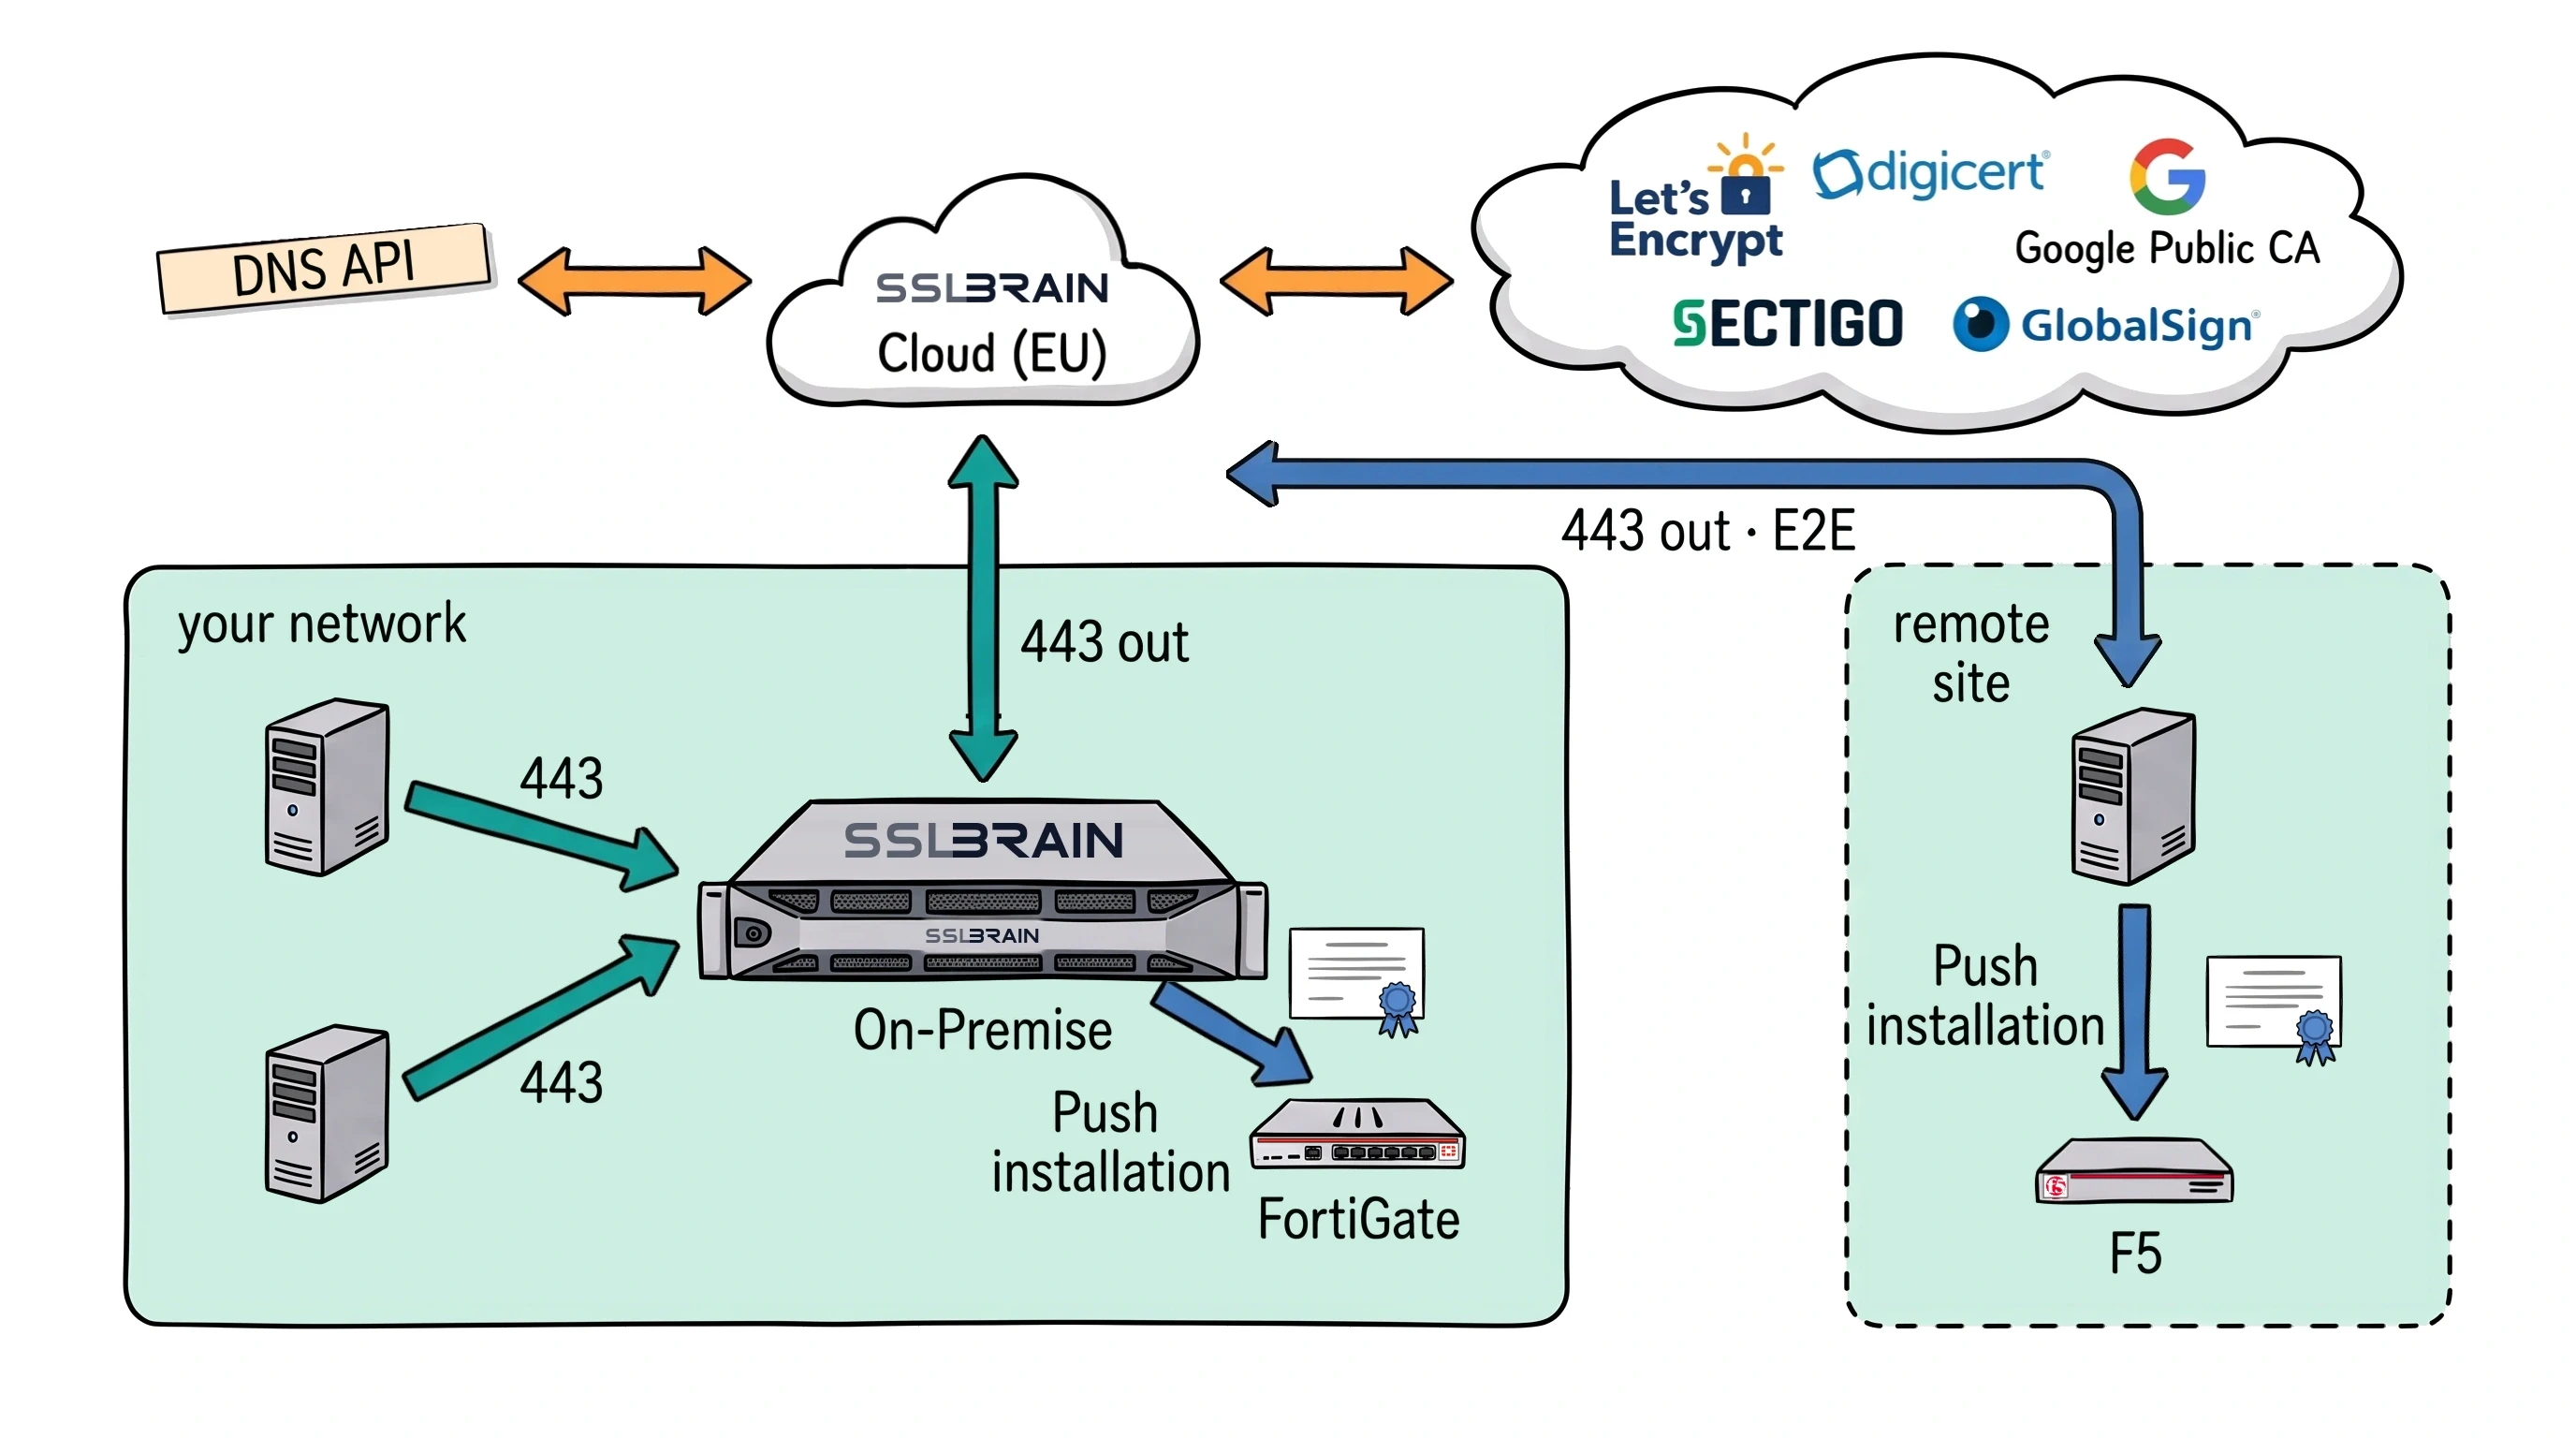
- Nothing is opened inbound: no network needs a port open from the internet.
- Through the firewall only outbound HTTPS on port 443 to sslbrain Cloud (EU), cloud.sslbrain.com.
- Easy to lock down: allow outbound 443 only to sslbrain’s fixed IP addresses. The security page in the manual lists every address and port sslbrain On-Premise uses.
- Service agents in the LAN connect directly to On-Premise on port 443. Service agents in a DMZ, at a remote site or at an external supplier connect via sslbrain Cloud (EU), E2E.
- Inside the network ports are still used, but only locally: On-Premise or a service agent pushes to equipment such as a NAS, firewall or F5 over SSH (22) or the device’s API (usually 443).
- Cloud talks to the CAs and DNS; On-Premise talks only to Cloud.
Network requirements
| Direction | Destination | Port | Purpose |
|---|---|---|---|
| Outbound | cloud.sslbrain.com | 443 | License validation, updates, vault |
| Outbound | acme.sslbrain.com | 443 | Certificate issuance |
| Outbound | registry.sslbrain.com | 443 | Appliance image for installation and updates |
| Outbound (local) | Your servers | Whatever ports your servers use for management (e.g. 22, 5985, 443) | The appliance installs certificates on your servers |
| Inbound (local only) | Browser and local servers/service agents | 443 | Admin UI for you, and the API your own servers and service agents call |
cloud.sslbrain.com, acme.sslbrain.com and registry.sslbrain.com use fixed IP addresses. The address list is in the manual under Security, Network. Inbound port 443 is only for access from your own network.