Step 5 of 8
5. Connect servers
Copy link to the page “5. Connect servers”Connect your servers so the appliance can find their services and install certificates on them.
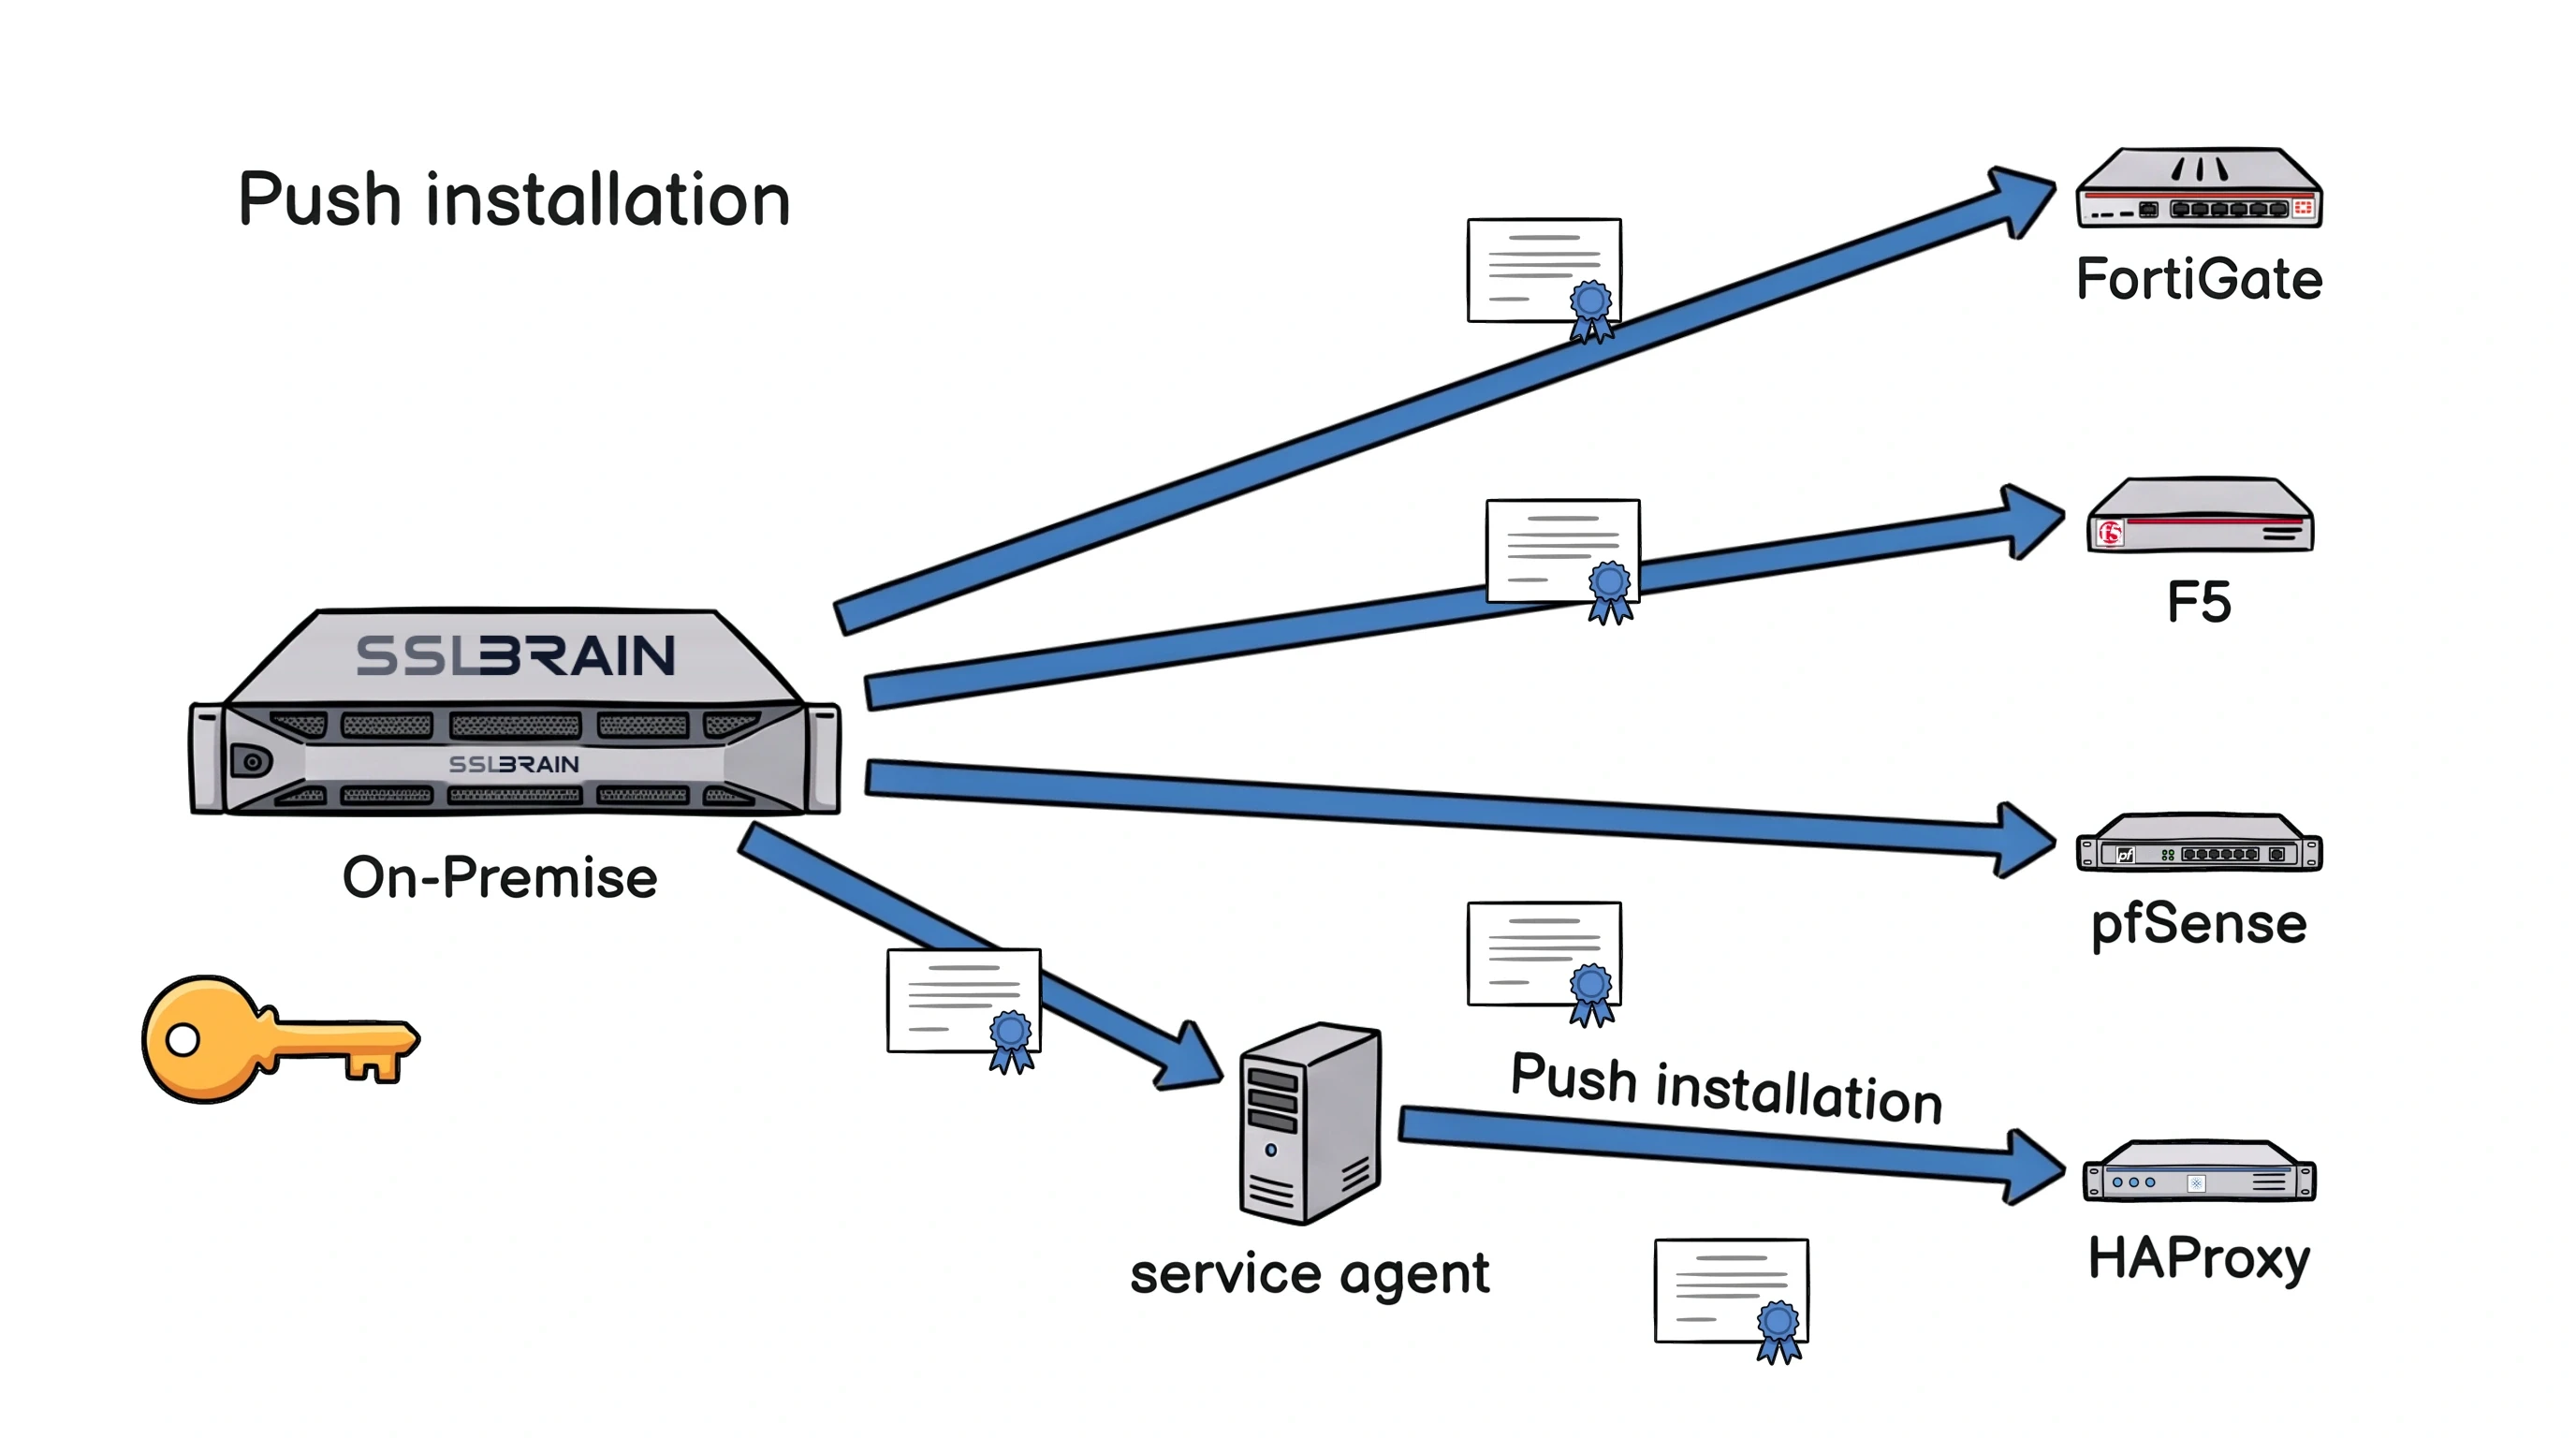
- Push installation: equipment that cannot run an agent, such as FortiGate, F5, pfSense, NetScaler and Palo Alto, gets the certificate from sslbrain On-Premise. It logs in through the device’s API (usually port 443) or over SSH (port 22) and installs it. Nothing is installed on the device.
- Windows and Linux servers get a service agent. It installs the certificate on its own server: IIS, Exchange, RDP and SQL Server on Windows, nginx, Apache and Postfix on Linux.
- From Professional, a service agent can also push to other servers and devices in its network, such as an HAProxy.
- Cloud services such as AWS, Azure and Cloudflare get the certificate from On-Premise through their API.
- On-Premise stores logins only for equipment without an agent, encrypted in its vault. Every delivery is checked, and if it fails, the certificate that was there before can be rolled back.
What you need
Copy link to the section “What you need”- Administrator access to the appliance and the server you want to connect.
- The server name or IP address.
How certificates are installed
Copy link to the section “How certificates are installed”- Locally via service agent: the service agent installs on the server where it runs.
- Push installation: the appliance connects to the server or device over SSH or an API and installs there. From Professional, a service agent in the same network can also push.
The service agent contacts the appliance over outbound HTTPS and checks integration signatures. You do not need to open an inbound port to it.
Connect the first server
Copy link to the section “Connect the first server”- Open Servers › Add server › With service agent.
- Follow Windows servers or Linux servers on the server. If it cannot run a service agent, follow Servers without a service agent.
- Open the server under Servers › All servers once installation finishes.
Servers without a direct connection to the appliance
Copy link to the section “Servers without a direct connection to the appliance”The two connection modes are directly to the appliance and via sslbrain Cloud (EU), E2E. For a server outside your network, follow the connection via sslbrain Cloud. See the addresses under How the service agent reaches the appliance.
Check that it works
Copy link to the section “Check that it works”The server appears under Servers › All servers. On the server page, Last check-in is up to date and services appear under Certificates once they have been found.
Next step
Copy link to the section “Next step”Continue with Prove the domain is yours.
If it fails
Copy link to the section “If it fails”- The server does not appear or its timestamp does not change → follow The service agent does not check in.
- The connection test reports an error or rejects the login → fix the connection or credential under The server cannot be reached.
- The server is waiting for approval → use the check below.
The server is waiting for approval
Copy link to the section “The server is waiting for approval”An install code normally approves the server. If it looks like a reinstall, it waits under Servers waiting for approval on Servers › Add server › With service agent. Compare Agent key with the key in the service agent log on the server, then click Approve if it is yours. Without an install code, the server waits under Servers › All servers. Only approve machines you recognise.
See which servers are ready
Copy link to the section “See which servers are ready”The Servers › All servers page shows connection, certificates, automation and status. The appliance appears as This appliance. Open a server to see Certificates, Installation plans and Connection.
Status Connected · Not automated means the connection works but the certificates need an installation plan. Click Create installation plans automatically, review the proposals, then create and start the selected installation plans. Status Connected · Automated means certificates are renewed and installed automatically.
Servers beyond your licence count are deactivated and receive no certificates. The licence covers the oldest servers first.
Find the services on the server
Copy link to the section “Find the services on the server”The appliance finds services and certificates after approval. They appear under Certificates and can be selected in the first installation plan. If you have added a service, choose Connection › Refresh server details.