Servers outside your network
Copy link to the page “Servers outside your network”Connect a server without a direct route to the appliance via sslbrain Cloud (EU), E2E.
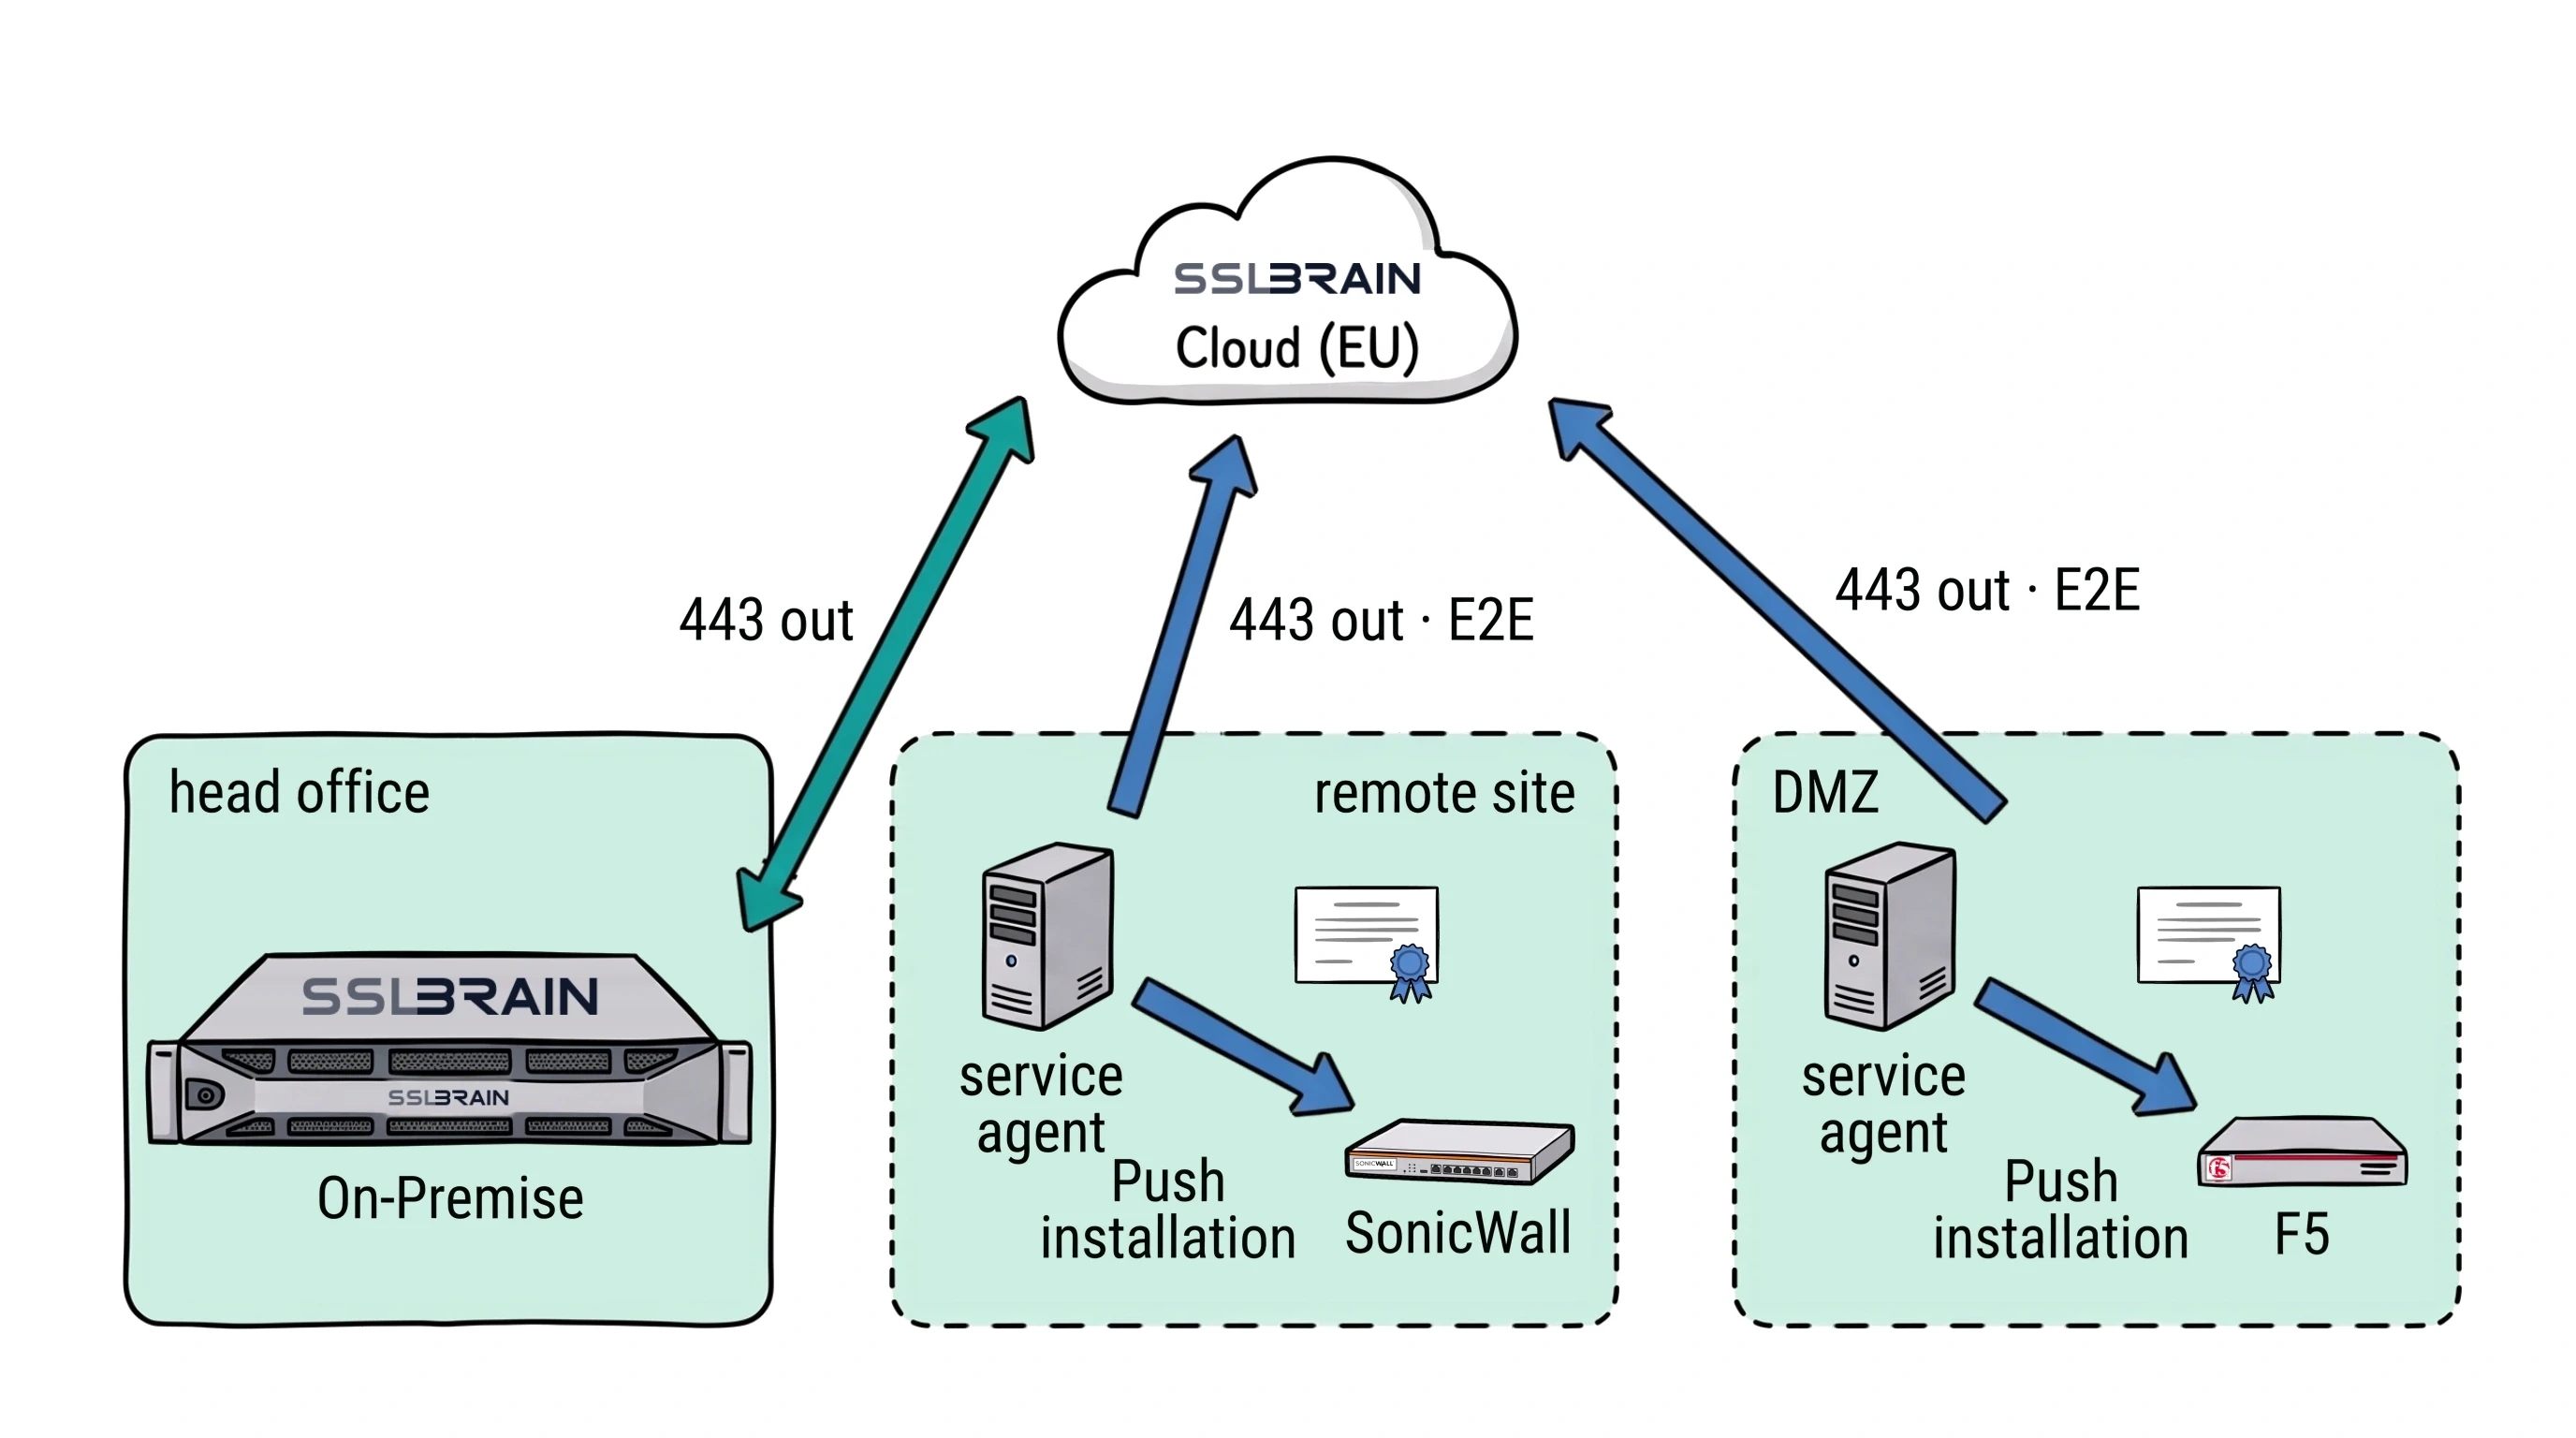
- The sslbrain On-Premise installation sits in the head office. Each of the other networks, such as a remote site, a DMZ, a data centre or a customer network, gets one service agent.
- Each network connects only outbound on port 443, through its own firewall, to sslbrain Cloud (EU). There are no connections between the networks.
- A service agent connects to On-Premise via sslbrain Cloud (EU), E2E: Cloud passes the messages on and cannot read them.
- The service agent installs certificates on its own server and pushes them to the equipment in its network, such as a SonicWall, F5, FortiGate or NetScaler.
- No VPN and no inbound ports. One service agent per network is enough.
What you need
Copy link to the section “What you need”- Administrator access to the appliance.
- An administrator login for the Windows server or a Linux account with sudo.
- Permission for outbound HTTPS on port 443 to
sslbrain.comandcloud.sslbrain.comfrom the server.
Connect the server
Copy link to the section “Connect the server”- Open Servers › Add server › With service agent and select the server platform.
- Open The server cannot reach the appliance directly, or has no internet and copy the command for connecting via sslbrain Cloud.
- Run the command on the server: in PowerShell as administrator on Windows or in a terminal with sudo on Linux.
- Open the server under Servers › All servers once it has checked in.
Both connections are outbound. You do not need to open an inbound port to the appliance or server.
Check that it works
Copy link to the section “Check that it works”The Service agent panel on the server page shows Cloud: Allowed, Cloud mailbox: Ready and Last reached: Through Cloud. The list under Addresses in use includes cloud.
Next step
Copy link to the section “Next step”Continue with Prove the domain is yours.
If it fails
Copy link to the section “If it fails”- The command via sslbrain Cloud is missing → enable Allow agent communication through Cloud under Appliance › Users and login › Login and sessions and check the appliance connection to sslbrain Cloud.
- The server is Blocked → open the server. Follow the message about licensing or a direct connection below.
- Cloud mailbox shows Cloud refused it; tried again in an hour → check the appliance connection to sslbrain Cloud. The appliance retries automatically.
- Cloud shows Opted out or Blocked locally on the machine → check the server’s own setting below.
- The server does not check in → check outbound port 443 to
cloud.sslbrain.comand follow The service agent does not check in.
Servers on other networks
Copy link to the section “Servers on other networks”The connection via sslbrain Cloud is used for servers in branch offices, at a hosting provider or behind a firewall without a direct route to the appliance. It can also provide fallback for a direct connection.
The licence blocks tasks
Copy link to the section “The licence blocks tasks”All licences can connect servers via sslbrain Cloud. Cloud connection is included in Professional and Enterprise. If the licence does not cover it, the server is Blocked and receives no tasks. Click Switch to direct if the server can reach the appliance directly, or Upgrade to change the licence. The server receives tasks again once it has connected directly or the licence covers Cloud connection.
A direct connection is tried first
Copy link to the section “A direct connection is tried first”The service agent uses the first working address in the list. With cloud last, sslbrain Cloud is used when the direct route fails. By default, the address changes after 3 failures and the first is retried after 1800 seconds. See retries and timeouts.
One server needs its own addresses
Copy link to the section “One server needs its own addresses”Open Settings for this service agent under Technical › Service agent on the server page. Edit Addresses in priority order (comma-separated, appliance for this appliance’s own address, cloud for sslbrain Cloud) and save. See settings for one server.
A service agent installed without cloud does not gain the connection automatically. An administrator can select Turn Cloud on again for this service agent. With CLOUD=deny on Windows, --cloud-deny on Linux or CloudDeny in a Windows policy, the service agent never contacts sslbrain Cloud, regardless of what the appliance sends. See MSI properties.
Turn off the connection via sslbrain Cloud
Copy link to the section “Turn off the connection via sslbrain Cloud”Disable Allow agent communication through Cloud under Appliance › Users and login › Login and sessions. Service agents that have connected directly continue directly after their next contact. Service agents that have connected only via sslbrain Cloud become Blocked but keep the connection so they can receive instructions to switch to direct. The page shows how many are affected.
Install codes cannot be used via sslbrain Cloud while the setting is off. A Cloud mailbox is removed once the service agent applies the configuration or after 30 days. If the connection is enabled again, each server’s own addresses and local opt-outs still apply.
The service agent needs updating
Copy link to the section “The service agent needs updating”Follow the update message on the server page. If it asks for installation on the server, use manual updating.
What sslbrain Cloud can see
Copy link to the section “What sslbrain Cloud can see”Messages are signed by the sender and encrypted to the recipient. The Cloud service can forward, delay or lose them, but cannot read them or create valid tasks. The install code contains the appliance fingerprint.
The Cloud service sees the installation ID, mailbox IDs, message sizes and times, and service agent public IP addresses. The Cloud service cannot read private keys or login credentials. See what else sslbrain Cloud sees.